
By the Swiss Applied AI & Cybersecurity Research Lab
Backed by


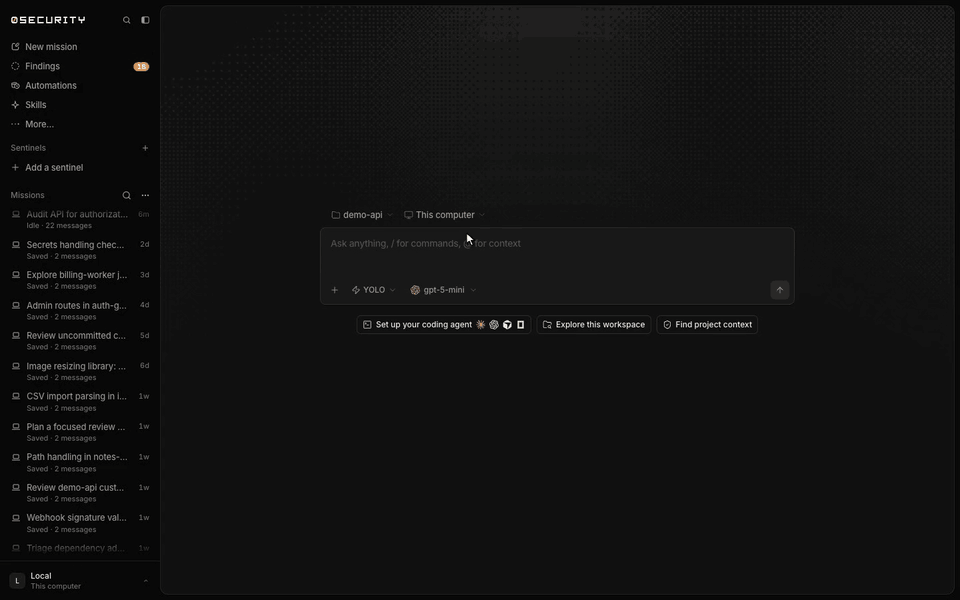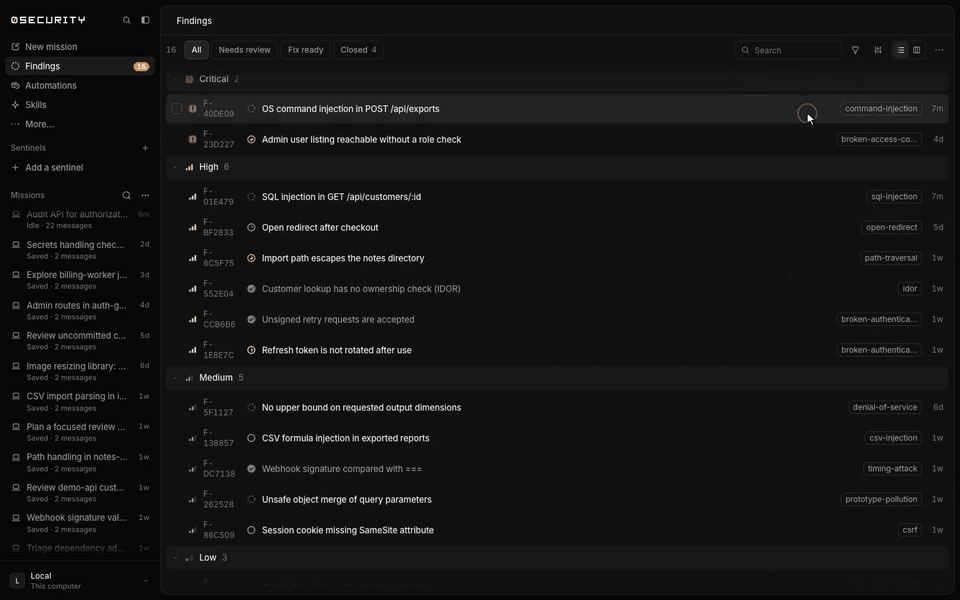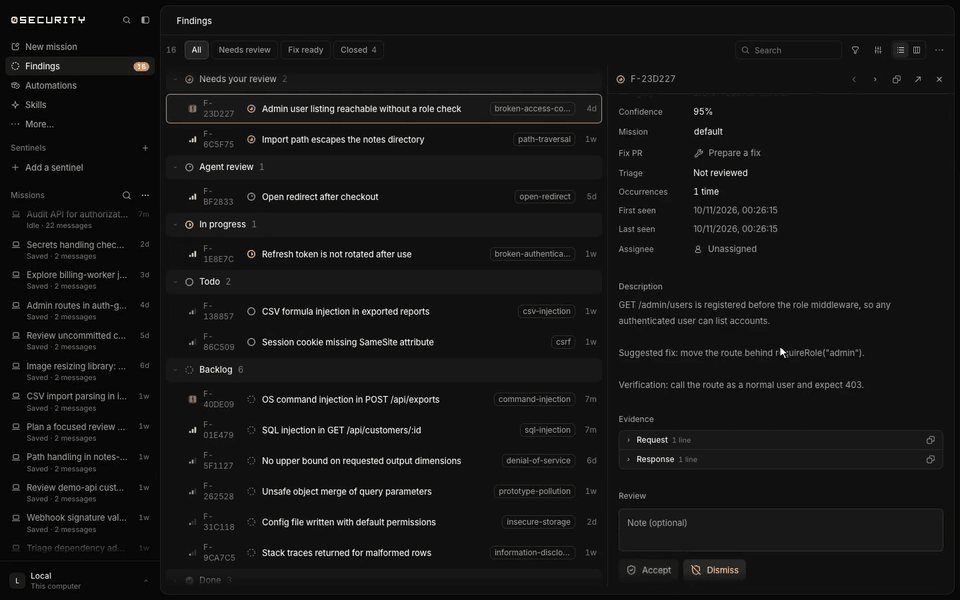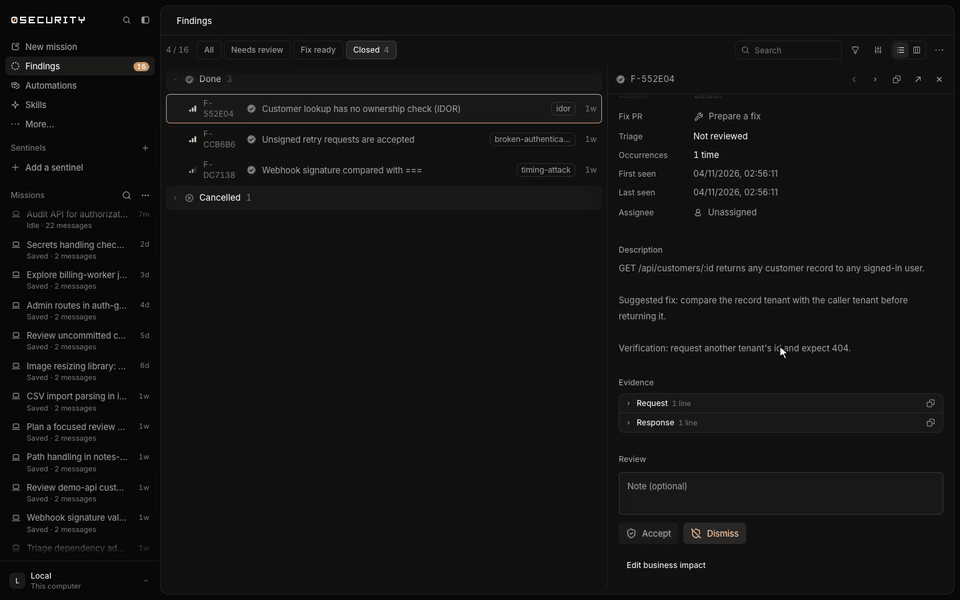
0security is an open-source framework for building and deploying security agents. They find vulnerabilities across your code, dependencies, infrastructure, LLM apps and AI agents, prove them, fix them, verify the fix and keep watching. It runs on your own infrastructure, with the LLMs you choose.


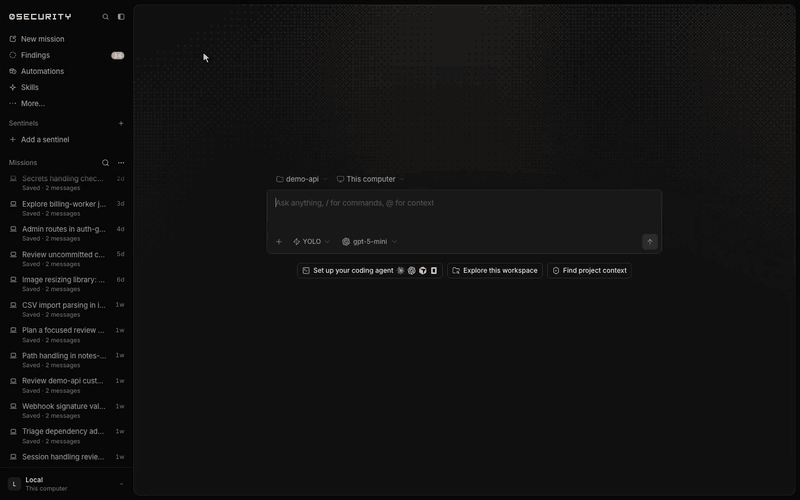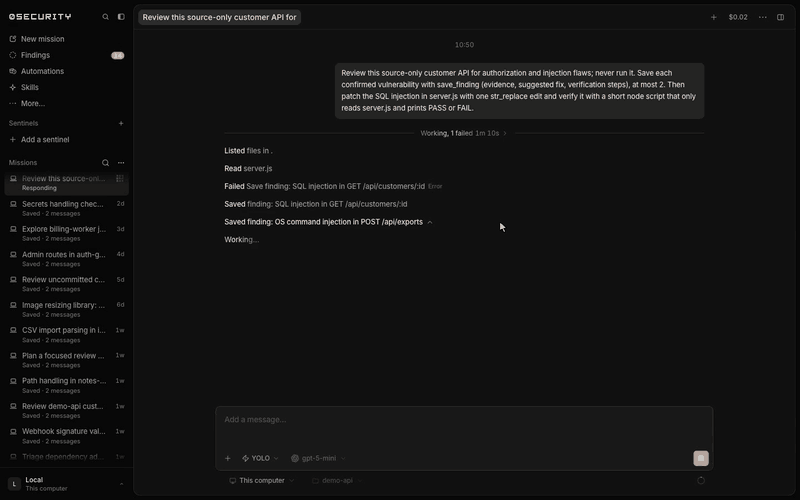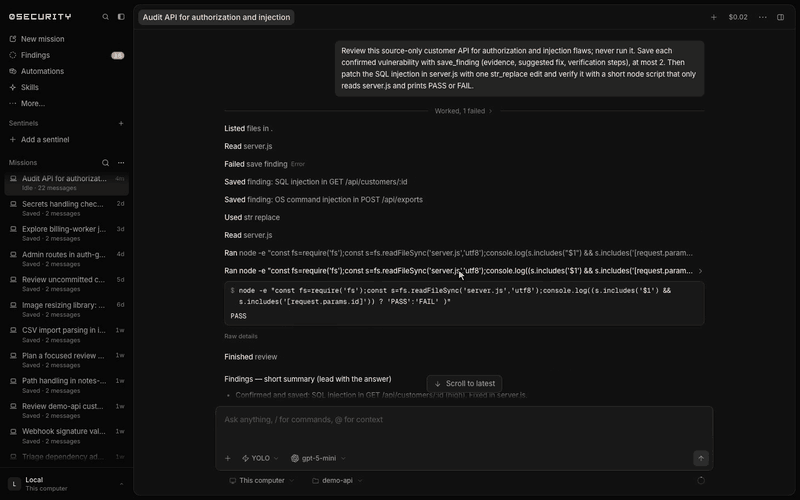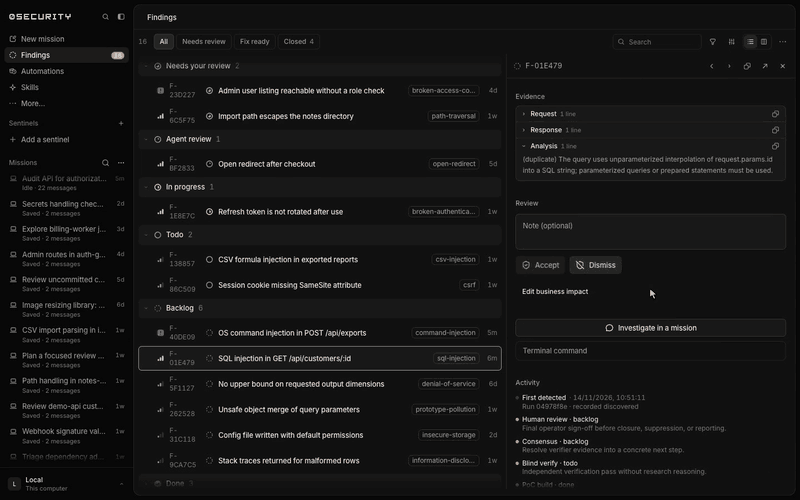
curl -fsSL https://raw.githubusercontent.com/0sec-labs/0security/main/install.sh | bash
0
Prefer the terminal?
export OPENAI_API_KEY="your-api-key"
0 scan source ./your-repo --runtime api --depth quick --cost-ceiling 2
Any supported provider works: set its key instead (Anthropic, OpenRouter, DeepSeek and more, see Models and keys), or connect one in the browser with 0.
Windows, Docker and source installs
- Windows (experimental): download
0-windows-x64.exefrom Releases. - Docker:
docker run --rm ghcr.io/0sec-labs/0security:latest --help. See the Docker guide. - Source: Node.js 24+ and pnpm, then
pnpm install --frozen-lockfile && pnpm build. install.shsupports Apple Silicon macOS and x64/ARM64 Linux. SetINSTALL_DIRto change the location.
Only scan systems you own or are authorized to test. See Scope & authorization.
- Find vulnerabilities in source code, web apps and APIs, MCP endpoints and packages
- Check dependencies with
0 scan deps scanand0 scan deps fixfor npm, pnpm, Cargo and PyPI - Hunt variants of a known fix across a codebase
- Reverse engineer binaries with Ghidra, plus kernel and memory-safety fuzzing
- Map your attack surface: domains, JavaScript, cloud and Entra ID posture
- Verify and fix: reproduce findings, generate patches and validate each one
- Build persistent security agents: Agents with a scope, budget and memory that run on a schedule or on every pull request, with skills, plugins and automations
- Disclose: assemble GHSA-ready advisory drafts from saved findings
- Test AI agents with prompt-injection campaigns
- Automate scans in CI/CD with JSON and SARIF output
- Extend it with plugins and skills, or drive it from coding agents over MCP
- Open source: MIT or Apache-2.0, built in the open
- Private: runs on your computer, in your CI or in a container, and only the context you send to your chosen model leaves it
- Flexible: any provider key or local OpenAI-compatible server, from the CLI, CI or a coding agent over MCP
- Evidence first: every finding links to its source evidence
- Verified fixes: patches are reproduced and validated before you apply them
- Proven in public: disclosed vulnerabilities and upstream fixes, including in the Linux kernel
0 automation run --template security-research \
  --target /absolute/path/to/repo --workspace /absolute/path/to/repo
0 lab mcp-server --automations --workspace /absolute/path/to/repo
See the CI/CD guide, plugins and MCP and the command reference.
- Documentation
- Scan modules
- Models and providers
- CI/CD guide
- Plugins and MCP
- Command reference
- Security research
- Enterprise
0 is built in the open. Huge thanks to everyone who has filed a bug, fixed a doc or sent a patch.
- Report bugs in issues
- Improve the docs
- Write a plugin or scan module
- Found a vulnerability in 0? See SECURITY.md
Start with the contributing guide. Run pnpm install and pnpm dev to work on the engine. Open an issue before large changes.